
Best Network Forensics Software for Security Analysts
 Oliver Ripka
The best network forensics software for a security analyst depends on two things: which stage of the investigation is slowing the team down, and how much infrastructure the team can operate. A solo analyst is usually best served by Wireshark, TShark, Zeek, Suricata, and NetworkMiner on a workstation; a SOC needs continuous sensors and packet retrieval such as Security Onion, Arkime, Corelight, or ExtraHop RevealX; and an incident response retainer team needs portable tools that work on whatever capture the client can provide.
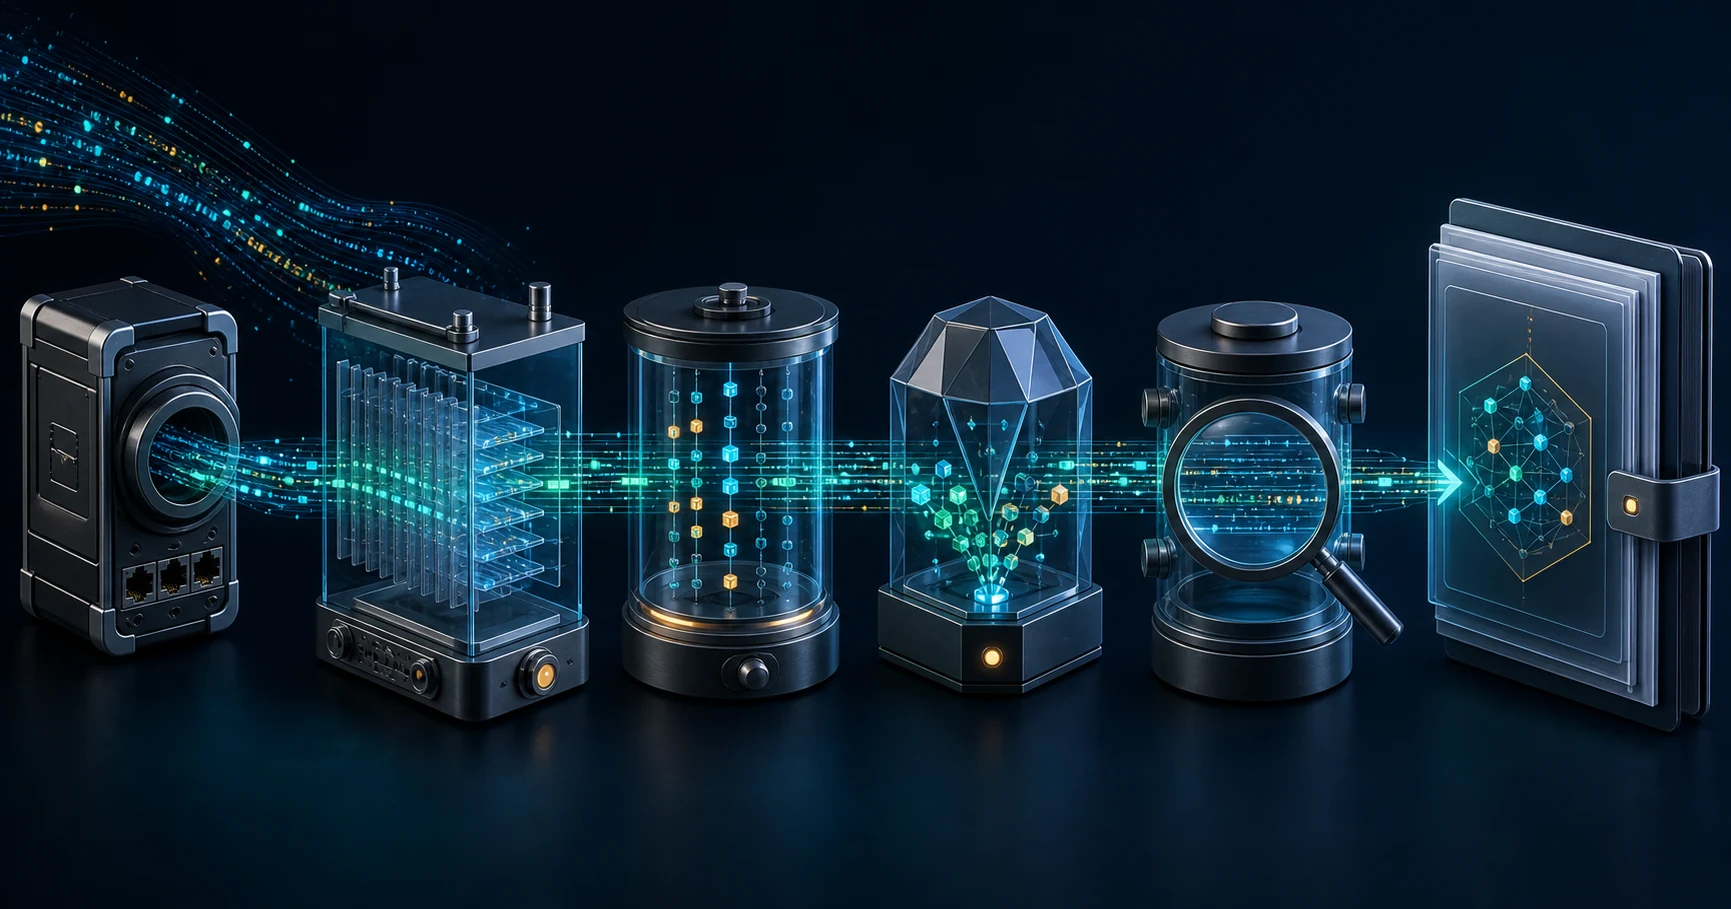
Our network forensics tools guide maps tools to the seven layers of a forensics stack. This article takes the analyst's view instead: what you do at each stage of a case, which software helps at that stage, and which stack fits your team.
Workflow stages and the software that helps
| Stage | Analyst question | Software that fits | Common failure |
|---|---|---|---|
| Intake | Is the capture usable for this question? | capinfos, Wireshark statistics, Zeek conn.log | Analyzing a one-sided or truncated capture without noticing |
| Scoping | Which hosts, times, and protocols matter? | Zeek, Arkime, Security Onion hunt views | Starting from the first alert instead of the incident question |
| Lead generation | Where are the suspicious events? | Suricata, Zeek, Corelight, ExtraHop RevealX | Treating a signature or fingerprint as a verdict |
| Reconstruction | What actually happened in the session? | Wireshark, NetworkMiner, Zeek file analysis | Losing track of which frames support which claim |
| Verification | Does the packet record support the conclusion? | Wireshark, TShark, PacketSafari Verification | Skipping the benign explanation |
| Reporting | What can responders act on? | Case system, PacketSafari Final Report | A narrative with no packet references or coverage statement |
Most teams already own decent lead generation. The stages that consume analyst hours are usually reconstruction, verification, and reporting, because they depend on expert time rather than sensor capacity.
Stage by stage
Intake: check the capture before trusting it
Record the capture source, duration, interfaces, and whether both directions are present. A quick check:
capinfos incident.pcap
tshark -r incident.pcap -q -z conv,tcp | head -40
Look for missing directions, packet slicing, large gaps in time, and drop counters if the capture tool reports them. These facts decide what you are allowed to conclude later.
Scoping: narrow the case
Turn the alert or report into a specific question: did this host contact command-and-control, move laterally, or send data out? Then reduce the capture to the hosts and window that matter. Zeek logs are a fast way to see who talked to whom, and Arkime or Security Onion let you retrieve the bounded PCAP from retained traffic.
Lead generation: let detectors do the wide search
Suricata can run rules over an offline PCAP and write EVE JSON. Zeek scripts flag notices and unusual protocol behavior. Enterprise NDR platforms such as Corelight and ExtraHop RevealX generate detections continuously across a sensor estate. Keep the output as a list of leads with timestamps and flow identities.
Reconstruction: rebuild the sessions
Use Wireshark to follow streams, read protocol fields, and check timing. Use NetworkMiner when the question is about recovered files, certificates, hostnames, or credentials. Hash every extracted object and open it only in an approved analysis environment.
Verification: test the conclusion against packets
For each decisive claim, find the frames that support it and ask what else could explain them. A periodic connection could be an updater. An SMB file write could be a legitimate deployment. Verification is where a lead becomes a finding or is closed.
PacketSafari builds this stage into its workflow: Triage runs capture-wide checks, the Agent investigates bounded evidence, and Verification tests the Preliminary Report against exact packets before the Final Report.
Reporting: hand off something responders can use
A useful report states the question, the conclusion, the exact packet evidence behind each claim, the alternatives considered, and the coverage limits. "No alert fired" is not the same as "no malicious activity," and the report should say which one you mean.
Recommended stack by team
Solo analyst or small security team
You need tools that run on one workstation, cost little to operate, and work on captures that someone else collected.
- Capture: tcpdump or dumpcap on the affected host, or exports from the firewall or cloud mirror you already have
- Leads: Suricata and Zeek run offline against the PCAP
- Reconstruction and validation: Wireshark, TShark, NetworkMiner
- Investigation and report: PacketSafari on the selected capture, when the time to reach a written, reviewable answer is the bottleneck
This stack is strong on depth and weak on history. You will only have the traffic someone thought to capture, so document that boundary in every report. The sibling guide on how to find malicious traffic in PCAPs gives filters and one-liners you can run with exactly these tools.
In-house SOC
A SOC needs continuous visibility, retention, and a repeatable path from alert to packets. Analyst time is shared across many cases, so consistency matters as much as depth.
- Capture and retention: TAPs or packet brokers feeding sensors, plus a packet recorder, Arkime, or Security Onion full packet capture
- Leads: Suricata and Zeek, or an NDR platform such as Corelight or ExtraHop RevealX
- Search and correlation: SIEM with network logs and Community ID or flow identifiers to join records
- Reconstruction and validation: Wireshark and TShark on retrieved PCAPs
- Alert verification and reporting: PacketSafari for selected alerts and captures, through the UI, CLI, or API, with a report the analyst can attach to the case
The common gap in a SOC is not detection volume. It is the step between "alert fired" and "analyst can defend a conclusion." Our walkthrough of Suricata alert verification through UI, CLI, and API shows one way to close it.
Incident response retainer team
An IR team works in other people's networks. You cannot assume sensors, retention, or a particular vendor. You need portable tools and a method that handles incomplete evidence honestly.
- Capture: tcpdump or dumpcap on client hosts, or exports from whatever the client operates, whether that is an NDR, a recorder, or cloud traffic mirroring
- Leads: Suricata and Zeek with your own curated rules and scripts, run offline on each delivered capture
- Reconstruction: Wireshark, NetworkMiner, and Zeek file analysis
- Investigation and report: PacketSafari on each delivered capture, with an on-premises deployment where client data cannot leave a controlled environment
- Sharing: pseudonymized sibling captures through Anoncap when evidence needs to go to a vendor or a third party
For an IR team, chain of custody and coverage statements carry extra weight because the client, legal counsel, or an insurer may read the report. Hash originals on receipt and keep derivatives separate. The sibling article on PCAP analysis solutions for network forensics covers those basics.
Where PacketSafari fits, and where it does not
PacketSafari is enterprise packet investigation for a selected capture. It does not capture traffic, does not monitor continuously, and does not replace Zeek, Suricata, Security Onion, an NDR platform, or Wireshark. It is useful at the reconstruction, verification, and reporting stages, when the capture exists and the team needs exact packet evidence and explicit coverage in a reviewable answer. The where PacketSafari fits page shows the handoffs.
How to evaluate network forensics software
- Write down the three case types your team handles most often, for example C2 confirmation, lateral movement, and data exfiltration.
- Time each workflow stage on a recent case. Find the stage where hours disappear.
- Shortlist software for that stage only, and check that it accepts the evidence you actually have.
- Test on a capture with known ground truth, including at least one benign explanation that looks suspicious.
- Score the output: exact packet references, alternatives considered, coverage limits, and export into your case system.
- Check operating cost: sensors, storage, tuning, updates, and the expertise each tool assumes.
Buy for the bottleneck, not for the longest feature list. A team with excellent detection and no time to verify alerts gains little from another detector.