Known indicators retain their source, revision, coverage, and exact packet or connection pivot.
- Suricata-compatible signature detection
- Stamus east-west and lateral-movement rules
- Offline IP, network, domain, URL, and file-hash intelligence

Enterprise packet investigation · Security
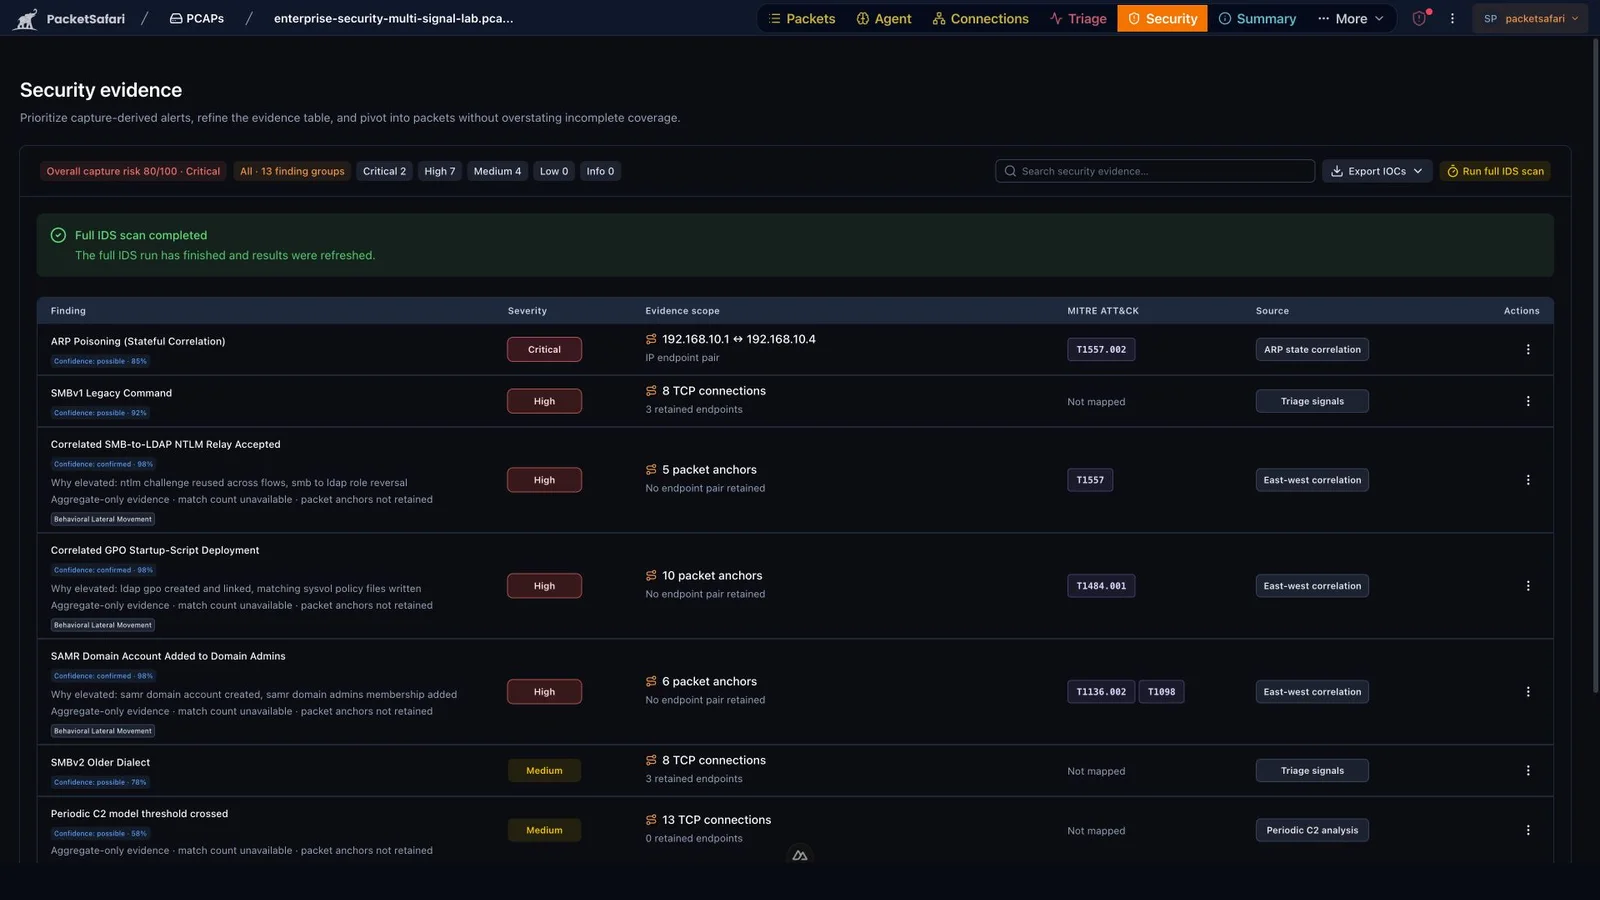
Upload a PCAP and combine signatures, offline threat intelligence, behavioral C2, tunnels, attack paths, and east-west findings with explicit coverage and exact packet evidence. PacketSafari complements live NDR, EDR, and XDR. It is not a continuous network monitor.
If the question is whether a firewall, IDS, IPS, proxy, or VPN action actually worked, use Security Control Validation.
Capture evidence available
Current evidence candidate
Encoded TXT queries form a sustained outbound transfer pattern.
dns.qry.type == 16 && ip.addr == 10.12.4.18Contain 10.12.4.18 and investigate the queried domain.
Living off the Network
Advanced actors increasingly target firewalls, VPN appliances, hypervisors, IoT, cameras, VoIP, and infrastructure where EDR cannot run or has weak visibility. Compromised systems become bridges through trusted protocols and encrypted paths.
Explanatory attack paths, not customer findings. Packet evidence complements endpoint and infrastructure telemetry.
SSH and SOCKS pivots
SMB, DCERPC, RDP, WinRM, and WMI
DNS, VPN, and encrypted sessions
Packet evidence beside endpoint telemetry
Security proof, counted
The PacketSafari Core Engine finds and preserves deterministic evidence. Agent focuses the investigation, explains the result, and guides the analyst back to exact packets.
The 54k+ and 27k+ claims remain the last qualified PacketSafari production-profile counts. Feed revisions and compatibility filtering can change both counts. Payload cadence remains qualification-only.
Investigation layers
Signatures, packet behavior, and cross-connection correlation stay distinct until the evidence supports a shared finding.
Known indicators retain their source, revision, coverage, and exact packet or connection pivot.
Independent packet behavior finds suspicious activity that a signature-only review can miss.
Cross-connection findings remain reviewable while emerging signals stay clearly qualified.
Security Triage
Prove the business case
Compare the team’s current investigation baseline with the same captures and questions in PacketSafari. No invented “faster” percentage.
Detection foundation
The PacketSafari Core Engine combines deterministic packet processing with AI investigation. It does not replace required IDS or behavioral processing with a model guess.
Choose quick partial screening or a separately tracked complete-capture verification milestone.
Correlate beaconing, DNS tunnels, covert channels, scans, lateral movement, and suspicious connection behavior.
Preserve local, ET Open, Stamus, and enabled Abuse.ch source provenance, revision, severity, and exact alerts.
Clean, partial, unavailable, and failed outcomes stay distinct; missing evidence never becomes a clean scan.
PacketSafari trains and tests its Agent on 150+ expert-curated PCAP investigations and protocol playbooks, shaped by 20+ years of real-world packet analysis.
Periodic beaconing findings are reported with supporting packet evidence and explicit coverage limits.