
Can Wireshark Use AI for Packet Analysis?
 Oliver Ripka
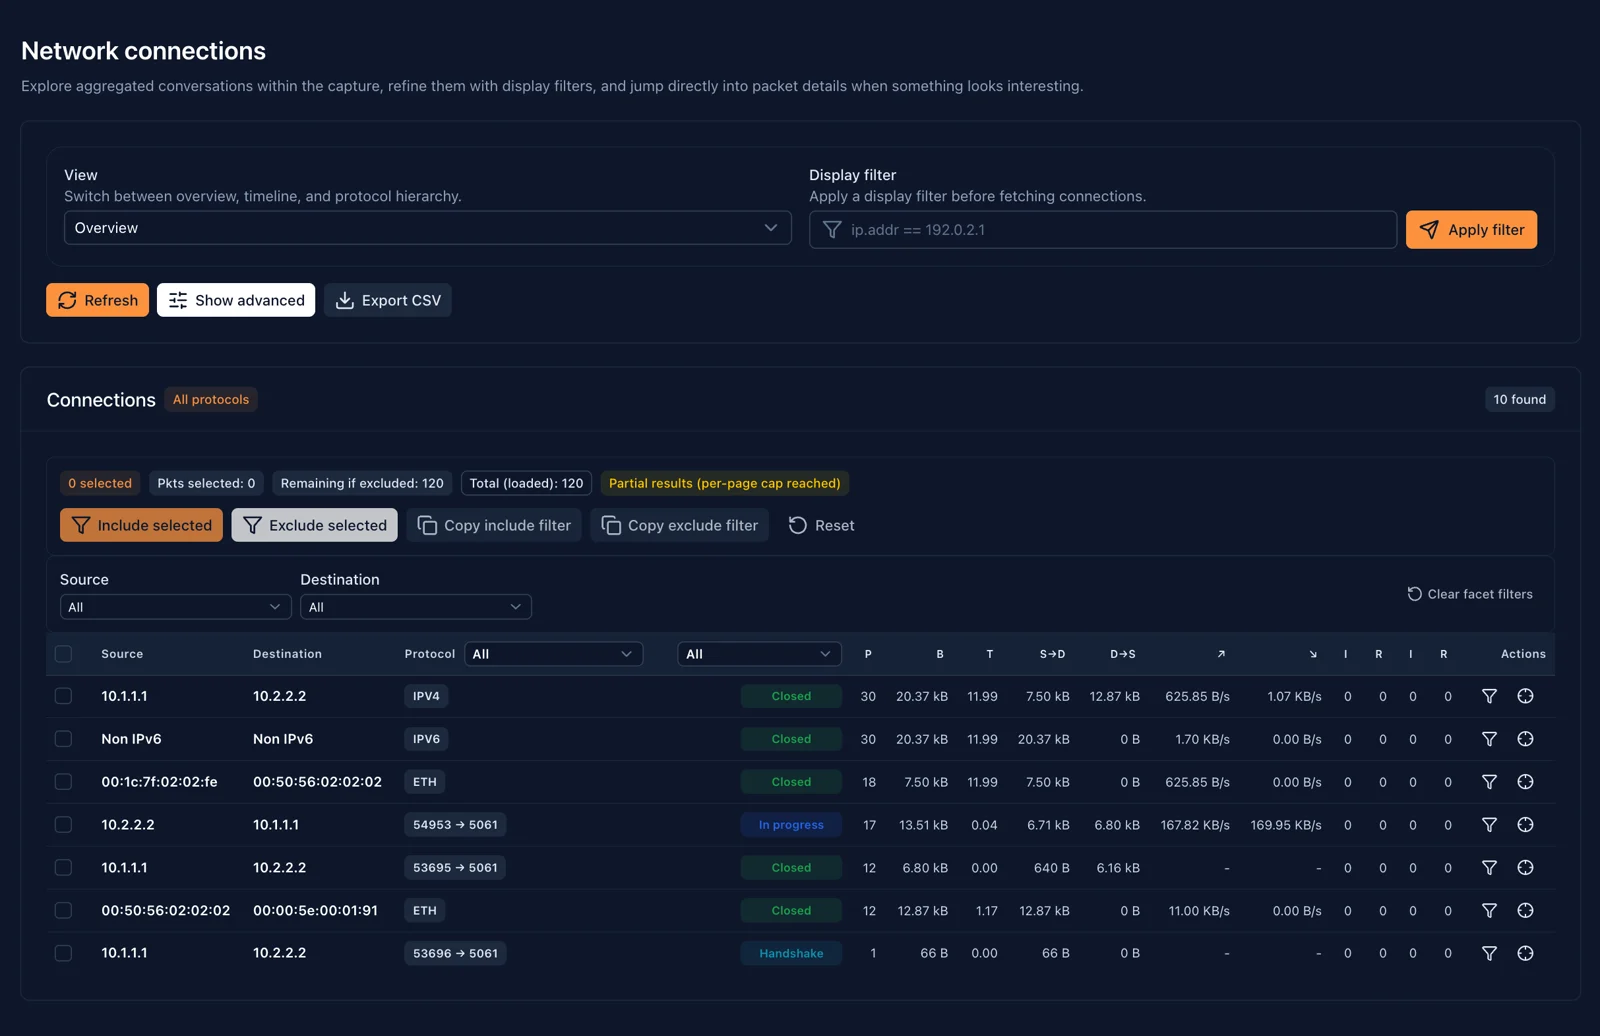
Wireshark itself does not ship a built-in AI assistant. Its official releases focus on dissection, filtering, statistics, and packet inspection, and AI is added around it: by exporting TShark output to a language model, by community plugins and MCP servers that wrap TShark, or by purpose-built investigation tools that use packet decoding underneath. Each option works for some jobs, and each needs a privacy decision before production traffic leaves your machine.
The earlier article Can ChatGPT Analyze PCAP Files? explains why a reliable AI workflow needs deterministic decoding, bounded tools, and verification. This article is narrower: what Wireshark provides today, the realistic ways to connect it to AI, and how to choose between them.
What Wireshark includes today
The Wireshark release notes and documentation we reviewed in September 2026 describe no built-in AI assistant, chat panel, or model integration. Development continues to focus on capture, dissectors, statistics, and the user interface. If a future release adds AI features, the release notes are the place to confirm it.
What Wireshark does provide is the foundation an AI workflow needs:
- Dissectors that decode hundreds of protocols deterministically
- TShark, which runs the same dissectors from the command line with text, field, and JSON output
- sharkd, a daemon that answers structured requests about a loaded capture
- Lua and C plugin interfaces, documented in the Wireshark Developer's Guide, for extending dissection and the interface
So the accurate answer is: Wireshark does not use AI on its own, but it is a strong decoding layer for AI tools built around it.
Realistic ways to add AI to a Wireshark workflow
| Approach | How it works | Good for | Main limitation |
|---|---|---|---|
| Copy and paste | Paste packet details or screenshots into a chat | Explaining one field, protocol, or error | Manual, partial, easy to lose context |
| TShark export to an LLM | Export summaries, fields, or JSON, then ask the model | Small, bounded questions about known flows | You choose what the model sees, and may miss the decisive packets |
| Community plugins | A Wireshark plugin sends selected data to a model | Convenience inside the familiar interface | Quality, data handling, and maintenance vary by project |
| MCP servers around TShark | A model calls tools that run TShark queries | Iterative questions where the model requests more evidence | Needs careful tool limits, sandboxing, and review |
| Purpose-built investigation tools | A product combines decoding, capture-wide checks, an agent, and verification | Unfamiliar or large captures, reviewable reports | A separate product to evaluate, deploy, and approve |
Export TShark output to a language model
The simplest reliable pattern is to let TShark do the decoding and give the model a small, relevant extract:
tshark -r capture.pcapng -q -z io,phs > hierarchy.txt
tshark -r capture.pcapng -q -z conv,tcp > conversations.txt
tshark -r capture.pcapng -q -z expert > expert.txt

tshark -r capture.pcapng -Y 'tcp.stream == 14' \
  -T fields -E header=y -E separator=, \
  -e frame.number -e frame.time_relative -e ip.src -e ip.dst \
  -e tcp.seq -e tcp.ack -e tcp.len -e tcp.flags.str -e _ws.col.Info \
  > stream14.csv

tshark -r capture.pcapng -Y 'tcp.stream == 14' -T json > stream14.json
Keep the frame numbers in every export. They let you check each model claim against the capture in Wireshark. Ask the model for hypotheses and next filters, not for a final verdict, and run any filter it suggests yourself before trusting it.
Community plugins and MCP servers
Several community projects connect Wireshark or TShark to language models, either as plugins inside the interface or as Model Context Protocol servers that expose TShark queries as tools for an AI client. These are independent projects, not part of the official Wireshark distribution.
Before using one, check:
- Where data goes. Which model provider receives packet content, and under what retention terms?
- What the tools can do. A tool that runs arbitrary shell commands is far riskier than one that only runs fixed TShark queries against a read-only file.
- What gets truncated. Many tools cap output to fit the model context. Silent truncation can hide the packets that matter.
- Whether citations survive. Does the answer reference frame numbers and filters you can reopen?
- Who maintains it. Plugins that lag behind Wireshark releases can break or misreport fields.
The MCP approach is promising because the model can ask for more evidence instead of receiving one fixed dump. It is also where tool boundaries matter most.
Privacy: anonymize before you share
Packet captures can contain credentials, personal data, internal addresses, hostnames, cookies, and business data. Sending a raw production PCAP, or a full TShark JSON export of one, to a hosted model is a data transfer like any other and needs the same approval.
Practical steps:
- Export only the flows and fields the question needs.
- Remove or truncate payloads where headers and timing are enough.
- Pseudonymize addresses and identifiers consistently, so flows still relate to each other.
- Confirm the model provider's retention, training, and regional terms with your security team.
- Prefer a local or on-premises model when policy does not allow external processing.
Anoncap creates a sanitized sibling capture that keeps diagnostic structure while replacing sensitive identifiers, and the guide on how to anonymize a PCAP covers the trade-offs. For teams that cannot send packet data to a hosted model, on-premises AI is the relevant deployment question.
What LLMs get wrong on raw packets
Language models are good at explaining protocols, proposing hypotheses, and writing clear summaries. They are weak at several things packet analysis depends on:
- Volume. Even a modest capture expands into far more text than fits in a model context. The model sees a sample, and may not know what was left out.
- Arithmetic across packets. TCP sequence and acknowledgment math, window scaling, and timing deltas are easy to get subtly wrong in text. TShark computes them deterministically.
- Invented references. A model can cite a frame number, field name, or display filter that does not exist. Every citation needs checking.
- Capture artifacts. Missing segments, one-sided captures, and NIC offloading can look like network faults. A model reading a summary rarely knows the capture boundary.
- Overconfident conclusions. A fluent root cause built on one strong pattern can ignore a contradicting baseline elsewhere in the file.
The fix is not to avoid AI. It is to keep decoding and counting in packet tooling, give the model bounded evidence, and verify what it concludes. The article on AI agents for packet analysis covers this design in more depth.
Purpose-built tools with exact packet citations
Purpose-built AI investigation tools take a different route from plugins: decoding, capture-wide checks, the model, and verification are designed as one system. PacketSafari is one example. Its Core Engine decodes the selected capture, Signal Scan and Triage Modules build a capture-wide Evidence Map, and the Agent investigates through bounded tools. The Preliminary Report is checked by an independent Verification step before the Final Report, and material claims cite exact packet evidence with explicit coverage.
That fits incident work on captures that are large, unfamiliar, or need a reviewable record. It does not replace Wireshark. Analysts still open the cited frames in Wireshark to inspect them directly, and PacketSafari investigates selected captures after the fact rather than monitoring traffic continuously. The where PacketSafari fits page compares it with other tool categories.
How to choose
- You need to understand one field or error: paste the decoded detail into a chat, then confirm in Wireshark.
- You know the flow and want a second opinion: export it with TShark, keep frame numbers, and check every claim.
- You want the model to explore iteratively: evaluate an MCP server with read-only, fixed TShark tools and clear output limits.
- You need a reviewable investigation of an unfamiliar capture: evaluate a purpose-built tool such as the PacketSafari Analyzer on a sanitized sample, and check whether its citations hold up in Wireshark.
In every case, decide on privacy first. For a fast manual orientation before involving any AI, the 15-minute guide to analyzing a PCAP covers capinfos, the Statistics views, and starter filters.